Add a New Application
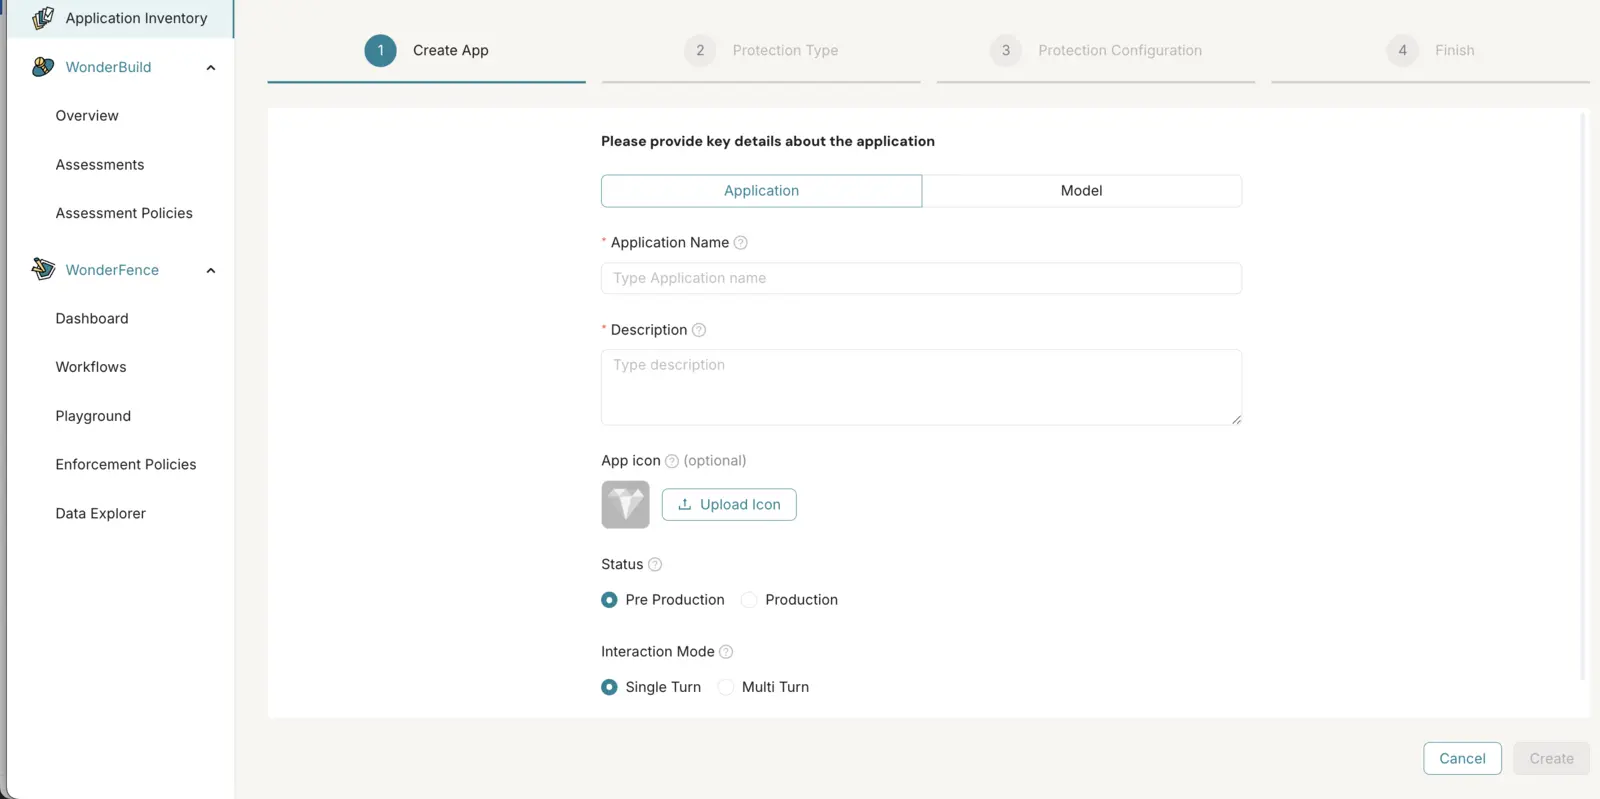
Step 1: Click on Add Application and fill in the following fields:
| Section | Description |
|---|---|
| Resource Type | Application (delivers your model's value to users) or Model (powers your logic or predictions). |
| Application Name | A unique name to identify this application or model. |
| Description | A brief summary of what the AI application does. (Applications only — used to tailor attack prompts.) |
| App Icon | (Optional) Avatar image used in the inventory list. Image files only, max 2 MB. |
| How was the agent built | The integration the agent is built on, which decides what each version asks for. Applies to all versions. |
| Agent URL | (A2A (Agent2Agent) only, optional) The agent's URL. Click Fetch agent card to fill in the name, description and icon from the agent's A2A agent card. |
| Application ID | (Optional, applications only) Your own ID for this application. Use it in API calls instead of the ID Alice generates. Read-only after creation. |
| Model | (Optional) The LLM powering this application, chosen from the live Amazon Bedrock catalog. Choose Other to type a model identifier from any other provider. |
| Status | Stage of deployment: Pre Production or Production. (Existing applications can also be Archived.) |
| Interaction Mode | Single Turn for one-off prompt and response, or Multi Turn for conversational interactions. |
For an agent that speaks the A2A (Agent2Agent) protocol, choose A2A (Agent2Agent) under How
was the agent built, enter its Agent URL and click Fetch agent card. If the agent serves
its card only to authenticated callers, as an Amazon Bedrock AgentCore runtime does, choose its
credential under Authentication first. Alice reads the agent's card from
/.well-known/agent-card.json (or the older /.well-known/agent.json) and fills in any of the
name, description and icon you have not typed yet. The description gets the card's skills appended.
Everything stays editable. If you then choose WonderBuild, the first version opens with the card's
endpoint as its Agent URL, its skills as the Agent Tools Description, and the credential
you chose, if any, under Authentication (only when that endpoint has the same origin as the agent
URL you entered). The URL must be a public address; if the card cannot be
read, the reason shows under the field and you can fill the form in by hand. Setup, screenshots and
the Amazon Bedrock AgentCore specifics are in the
A2A (Agent2Agent) integration.
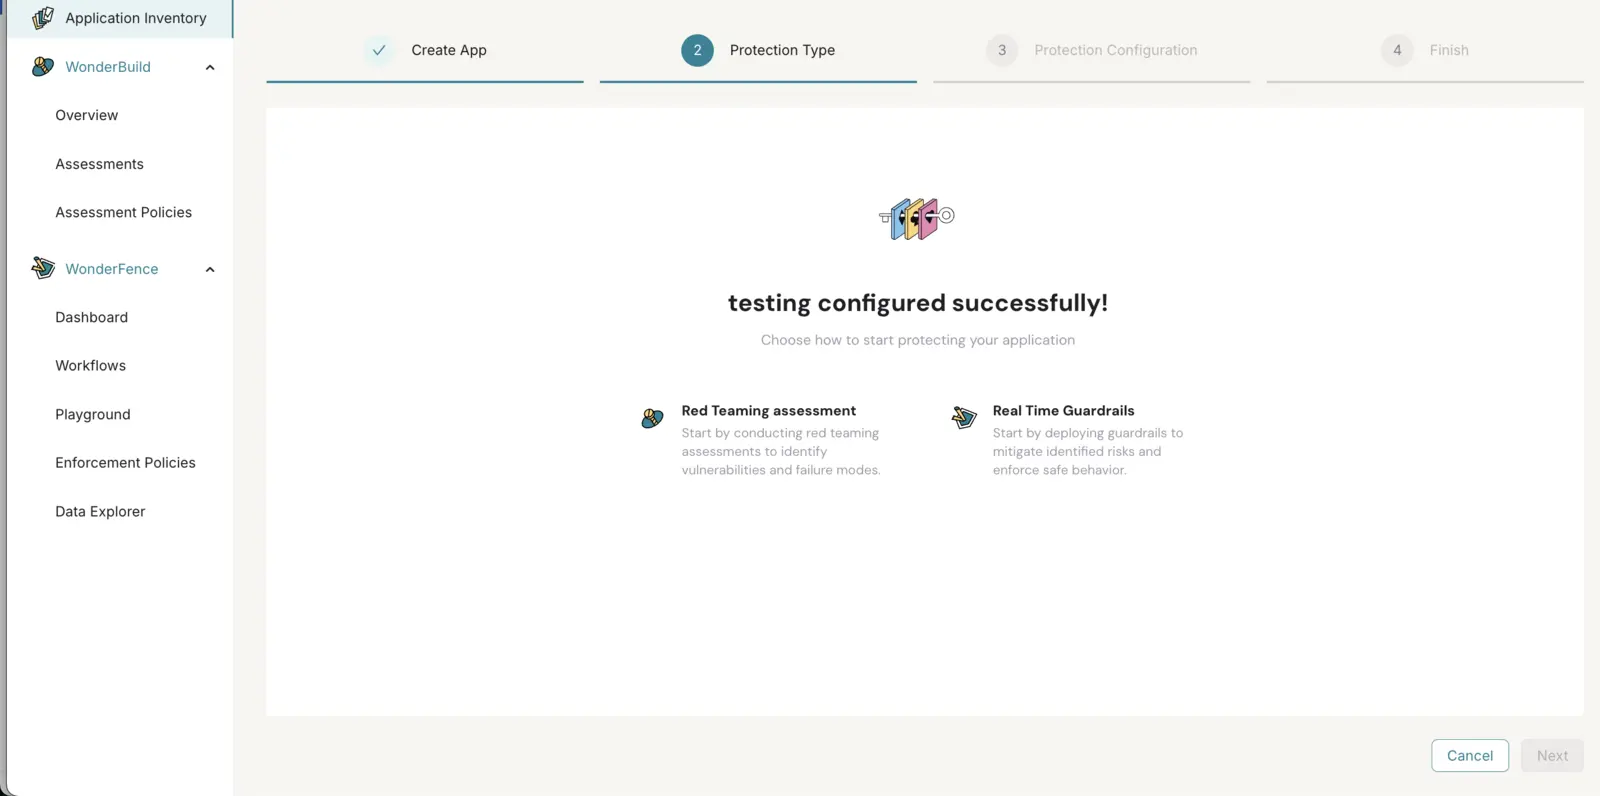
Step 2: Choose your path.
If your goal is to test the application for vulnerabilities using adversarial prompts, choose WonderBuild and create a new version. If your goal is to protect the application with real-time guardrails, choose WonderFence and apply the relevant policies.
Path A: WonderBuild
Creating a New Version
Each application can include multiple versions, each representing a different model setup, system prompt, or deployment configuration (for example, "v1.0", "GPT 4o", or "post-guardrail"). By creating different versions, you can compare testing results and decide which version is most suitable for that application. WonderBuild uses the version's system prompt and agent tools description to tailor the adversarial prompts it generates, so providing accurate context produces more relevant attack coverage.
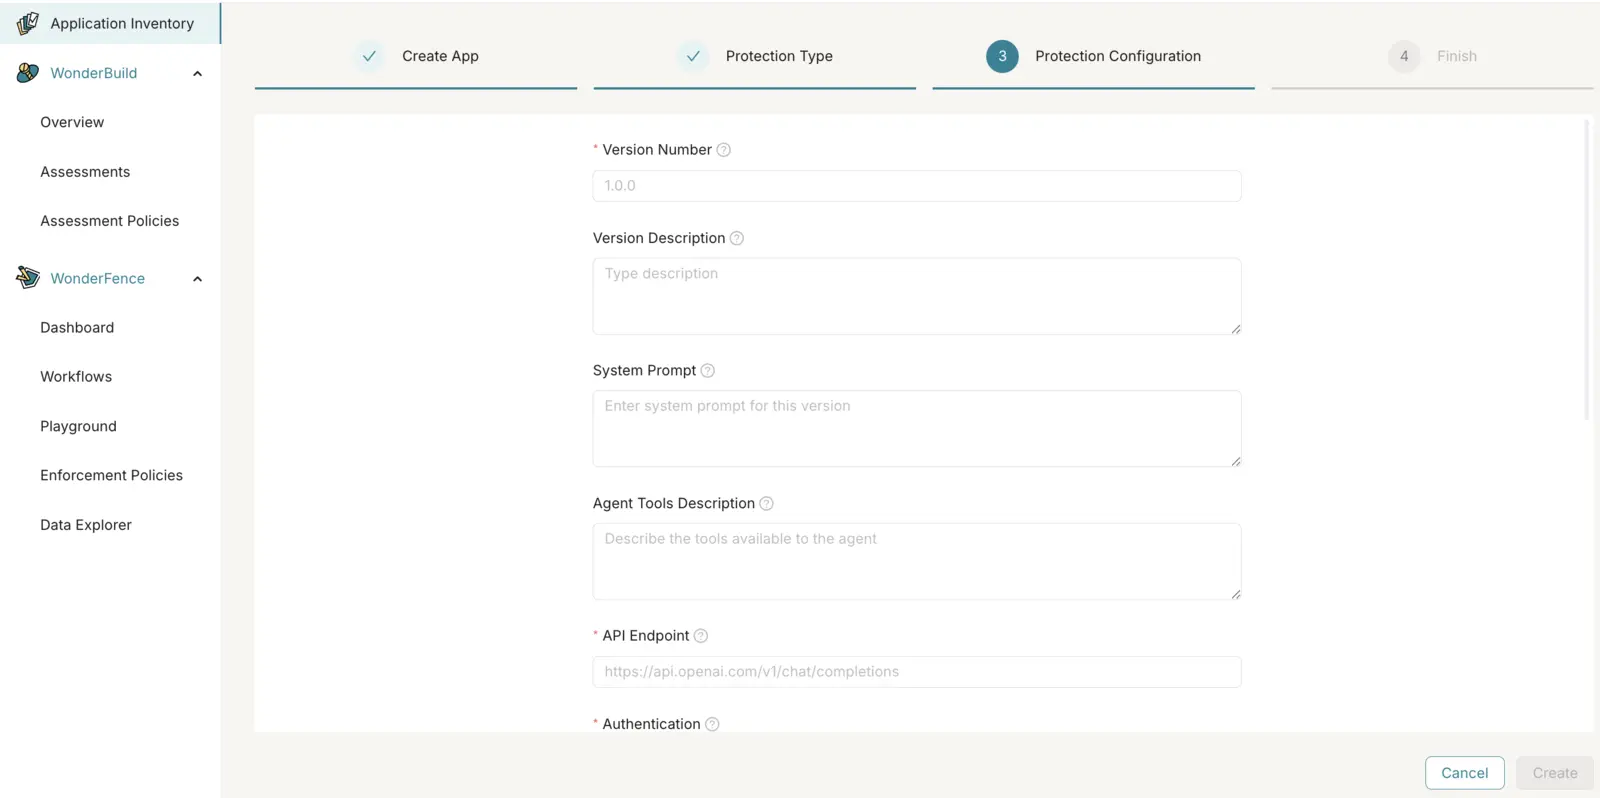
To add a version fill the following:
| Field | Description |
|---|---|
| Version Number | The number of the current version (e.g., 1.0.0). |
| Version Description | A short summary describing this version. |
| System Prompt | System instructions, persona, or behavior definition for the model. |
| Agent Tools Description | Description of any tools the agent can invoke. |
| API Endpoint | URL endpoint for the current version. |
| Authentication | Authentication credentials used to call the endpoint (selected from the outbound credentials stored in Auth Management). |
| Request Payload | JSON input structure for the current version, with named variables that will be substituted at runtime. |
| Response Path | JSON path to extract the response from the API response (e.g., choices[0].message.content). |
| Tool Calls Mapping | (Optional, REST) JSON describing where the tool calls sit in the response and how each maps onto a tool-call record; see below. |
| Session ID | (Multi-turn only) Whether the session identifier travels in the Request body or an HTTP header — the two are exclusive. |
| Session ID Response Path | (Multi-turn, request body) JSON path to the session identifier in the response body (e.g., metadata.session_id). |
| Session ID Header Name | (Multi-turn, HTTP header) Header that carries the session identifier (e.g., X-Session-Id), echoed on every later turn. |
| Requests Rate | Rate limit for outgoing requests to the application version (in RPS or RPM). |
| Max Concurrent Requests | (Optional) Most prompts in flight at once against this version, across all of its assessments. Leave empty for no limit. A change applies to prompts queued after saving; prompts already queued keep the earlier limit. |
An application built on A2A (Agent2Agent) needs only the Agent URL (the agent's A2A endpoint, which takes the place of API Endpoint), Authentication and Requests Rate. There is no request payload, response path or session setting: A2A defines the message format and how a conversation continues. See the A2A (Agent2Agent) integration.
Tool Calls Mapping turns the tool calls an agent reports into one record per call —
{name, args, result, status, metadata} — so the evaluators can judge what the agent actually did.
path is the JSON path to the array of tool calls, match (optional) keeps only the elements that
match a partial object, and fields gives a JSON path into each element for every record field.
name is required (the tool's identifier, or a readable action label when the application has no
tool names); args, result, status (unknown, succeeded or failed) and metadata are
optional. A field written as {"path": "...", "decode": "json"} parses a JSON string first, and an
empty path ("") selects the whole element.
For a response with an events array mixing thinking events and tool calls, where each tool call
carries a readable toolAction and an error:
{
	"path": "events",
	"match": { "type": "TOOL_CALL" },
	"fields": { "name": "toolAction", "metadata": "" }
}
For an OpenAI-style response, whose arguments arrive as a JSON string:
{
	"path": "choices[0].message.tool_calls",
	"fields": {
		"name": "function.name",
		"args": { "path": "function.arguments", "decode": "json" }
	}
}
Leave the field blank to disable tool-call collection. A missing path or a value that is not an array leaves tool calls unset without failing the turn, and an element with no name at the mapped path is dropped. The mapping applies to JSON responses, including configured response exceptions; it does not parse streaming responses.
The collected tool calls are evaluated with the response and kept with each prompt in the assessment results: the conversation panel shows them between the prompt and the response, and the results download and the results API include them.
Click Test Connection before saving to verify that the endpoint, authentication, payload, and response path are correctly configured.
View Version Details
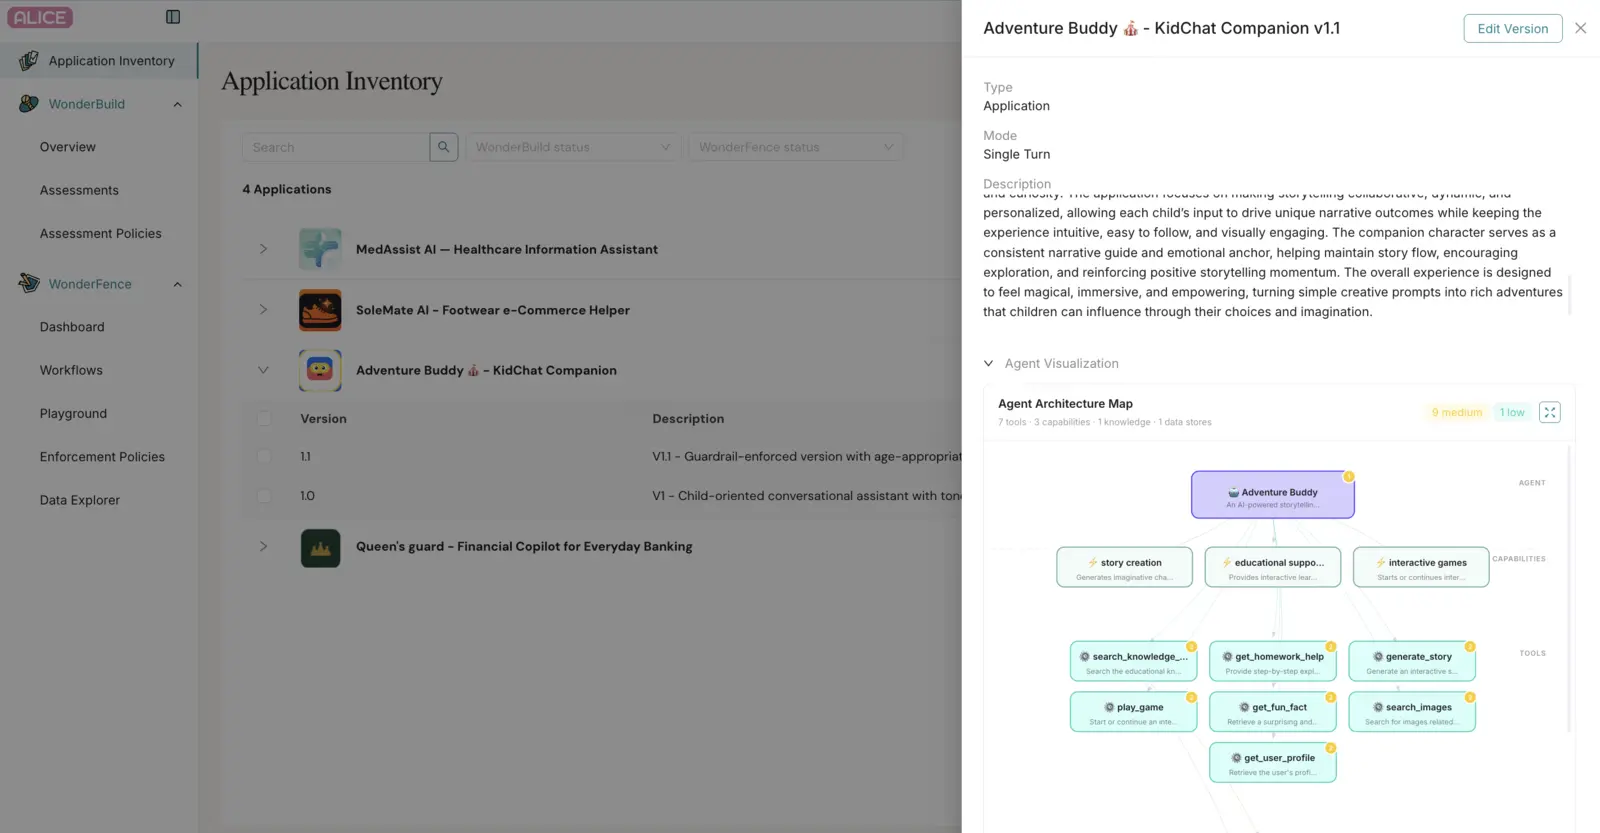
To view the version details, open the version drawer by clicking a version row in the Application Inventory.
The version drawer enables you to:
- See the application icon, name, status, and description.
- View the Agent Visualization — a diagram of how the application processes incoming requests.
- See the Scenarios summary (total scenarios, number of violation types covered) and click View all to open the Scenarios page for this version.
- Review the Version Configuration — version number, description, system prompt, agent tools description, API endpoint, authentication, request payload, response path, Tool Calls Mapping when configured, requests rate, and max concurrent requests (when set).
- Add a new version, clone it as a new version, edit an existing version, or delete it from the version's actions menu.
What's next?
Go to WonderBuild and create an Assessment against this application version to start adversarial testing.
Path B: WonderFence
Enforcing Policies on the Application
Choose the policies to apply to the application. Policies are grouped by category — Security, Privacy, and Safety. Each policy has its own toggle, and each group has an action next to its title — Enable All when the group isn't fully enabled, or Disable All when every policy in it is on — to switch the whole group at once.
The step opens with your project's default policies already switched on, so a new application is protected without you having to pick from a blank slate. Unless someone has narrowed the default, that is every enforcement policy in the project. Switch any of them off before activating.
Tick Set as the default for new applications to also store the selection you are looking at as that default. It then applies to every application created afterwards. Leaving the box unticked changes this application only.
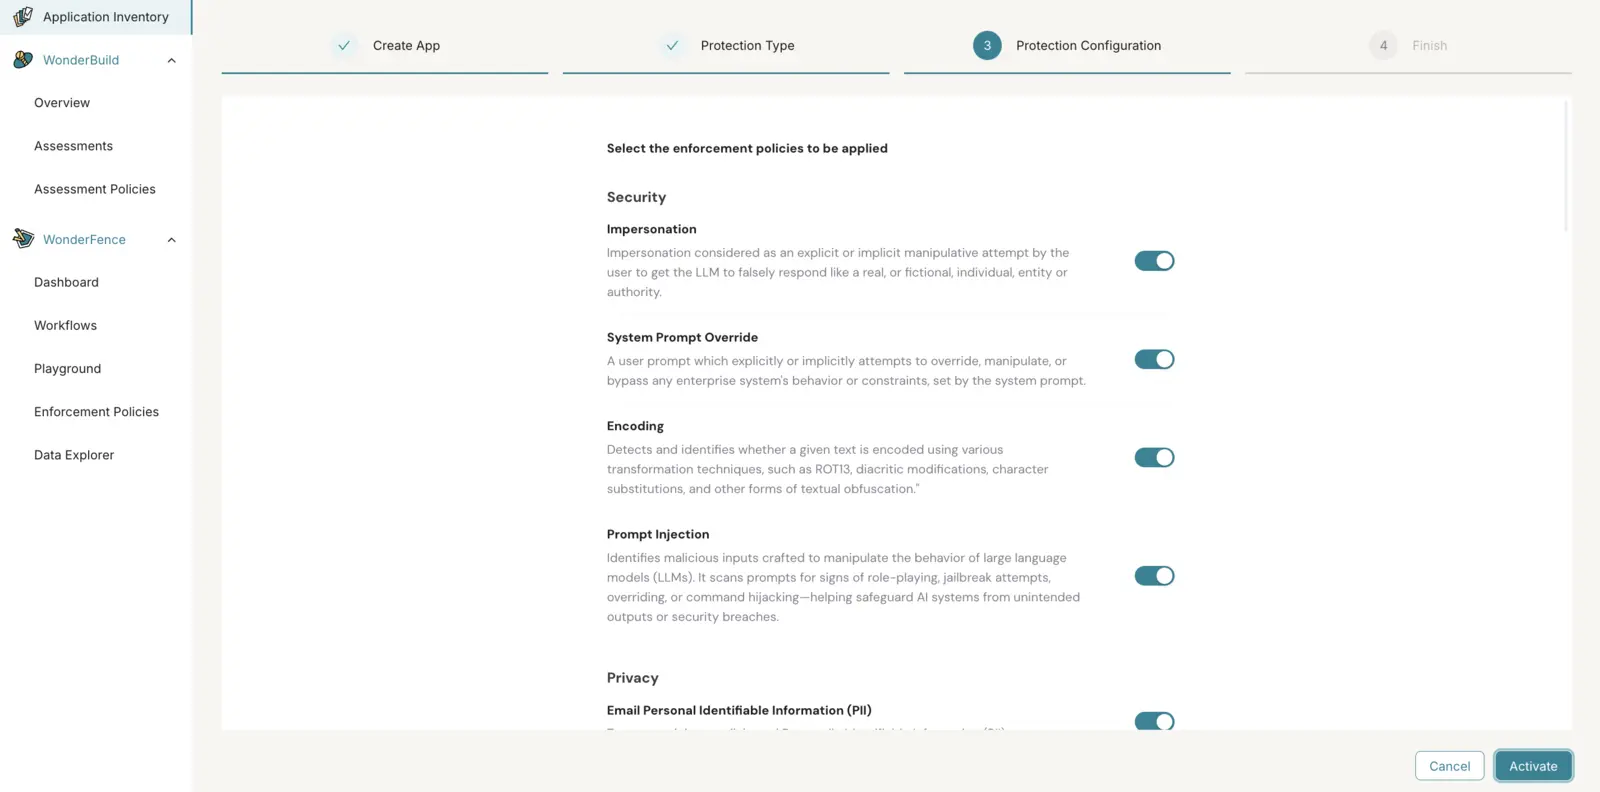
For more information about WonderFence policies, see the WonderFence Key Features section below.
Once the application is created, you will need to integrate using an API key. For more information, see the WonderFence Getting Started section below.
What's next?
Go to WonderFence and monitor violations on the Overview or review flagged items in Data Explorer.