Assessment Policies
The Assessment Policies page is the centralized interface for managing the assessment policies used during WonderBuild assessments. Each policy is tagged with a Type — Safety, Privacy, or Security — and is either a built-in System policy provided by Alice or a Custom policy you create.
You can:
- Search for a specific policy by name.
- Narrow the list from the panel on the left: a category under Category Presets (Security, Safety or Privacy), or a framework under Frameworks (OWASP or MITRE). Each item shows how many policies it holds. Selecting an item shows only its policies; click it again to return to the full list.
- Build your own preset: click Add Preset at the bottom of the rail, name it, tick the policies it runs and click Save. It appears under Custom Presets; select it to Edit Preset (rename it or change its policies) or Delete Preset. A preset name must be unique among your project's WonderBuild presets; a WonderFence preset may share it.
- Filter policies by risk and by source (System or Custom) from the filters above the list.
- Read the list by category: policies are grouped under a header for each category (such as 12 Security), and the count above the list shows the total.
- See on each row whether the policy is System or Custom, the content it covers (Text, Image, Audio or Video) and how many risks it maps to in each framework (such as OWASP 2); hover the framework count to see the risk codes. When the list is narrow, these details are hidden one at a time so the policy name stays readable.
- Switch between a list view and a card view using the view toggle above the policies; your choice is remembered for next time.
- Create a new custom policy.
- View the read-only details of any policy.
- Edit, duplicate, or delete your custom policies. System policies can be duplicated to create an editable copy.
Create a policy:
Clicking Create Policy opens a full-page, two-step wizard: Create Policy followed by Train Policy. Step 1 collects the policy definition:
| Field | Description |
|---|---|
| Policy Name | A concise name representing the policy. |
| Type | The policy group the policy belongs to. Required — choose Safety, Privacy, or Security. |
| Policy Guidelines | Specific guidelines or criteria that define what constitutes a violation of this policy. Must be at least 100 characters — a live character counter under the field shows your progress toward the minimum. Use Upload from File to populate the guidelines from a .txt or .pdf file. |
Once the definition is valid, Next advances to Train Policy. Arriving there drafts your policy and generates example attack prompts with the responses your application might give, which takes about a minute; the step shows what it is doing while it works. If that cannot be completed, the step says so and offers Try again — nothing has been created at that point, and you can also go back to adjust the definition and start over.
Each example shows the prompt above the response, with the proposed Verdict on Response — Benign or Violative. Confirm (👍) or reject (👎) each one; rejecting flips the verdict, and you can add an optional note explaining why from the card's ⋮ menu. Training runs over two rounds, shown above the list as Round 1 of 2, and each round is generated from your verdicts on the one before it. On the final round, Next confirms your verdicts and the button becomes Create. Your verdicts are used to rewrite the policy, so the guidelines saved on the created policy are a fuller version of what you wrote on step 1. Creating the policy returns you to the catalog, where the new policy is briefly highlighted.
When editing or duplicating a policy, a dialog opens with the name and guidelines; the Type is not shown and stays as originally set. Duplicating pre-fills the name as Copy Of <source policy>, which you can rename to anything you like, and pre-fills the source's guidelines — you must edit the guidelines before the copy can be saved, so each copy is meaningfully distinct.
To open a read-only view of a policy's name, type, and guidelines, click anywhere on its row, or use the row actions menu (⋮) and choose View Details. This is available for both System and Custom policies. When viewing one of your own Custom policies, the details view also offers an Edit Policy button that switches it into edit mode in place.
→ Go to Assessment Policies page
First Assessment Walkthrough
Step 1 — Register Your Application or Model
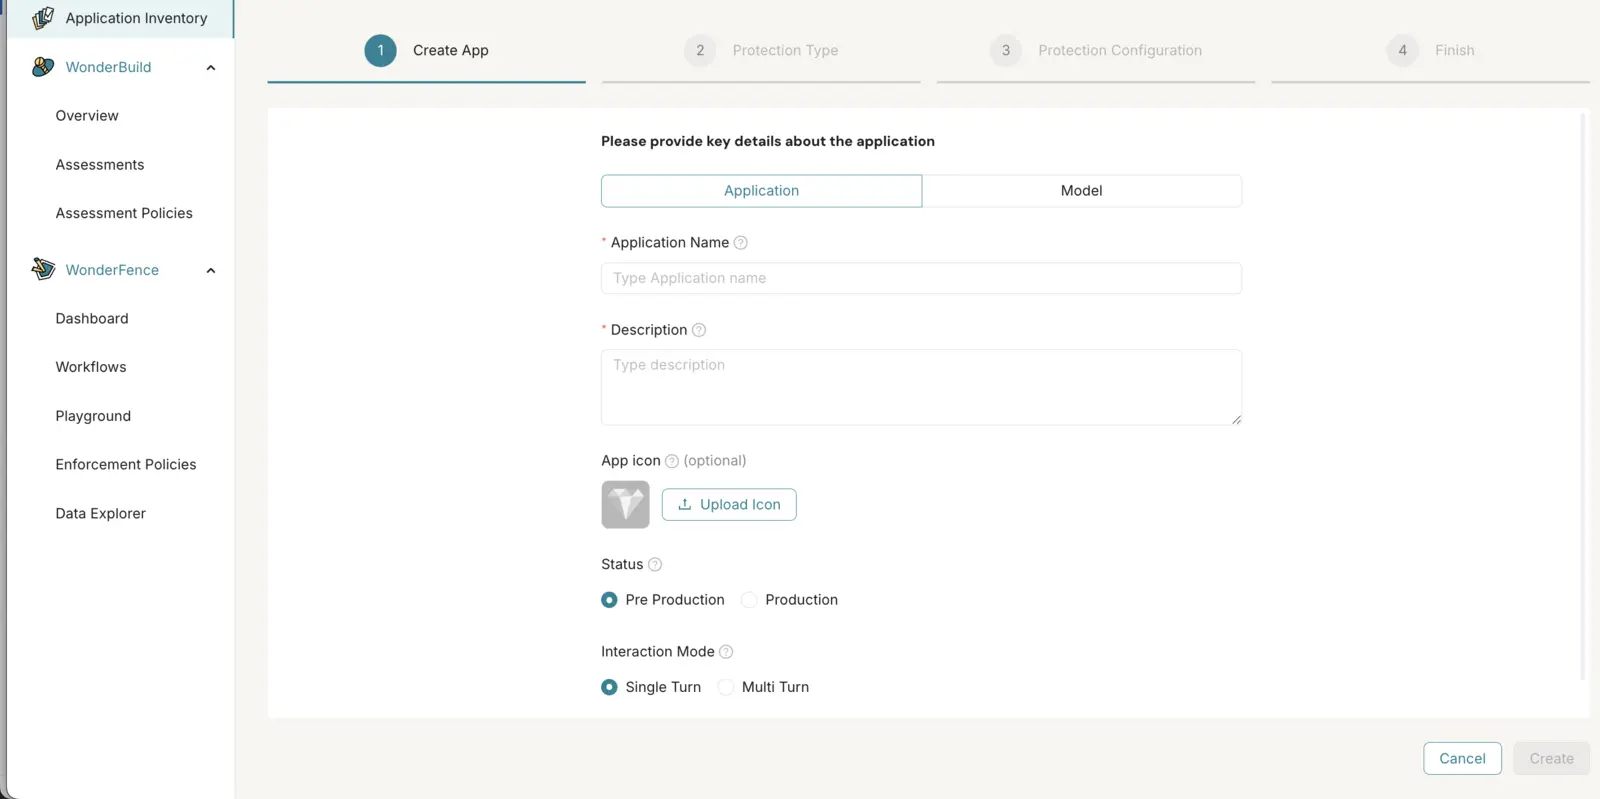
From the Application Inventory page, click Add Application and fill in the application details (Resource Type, Name, Description, Status, Interaction Mode). See Application Inventory for the full field reference.
Step 2 — Configure a Version
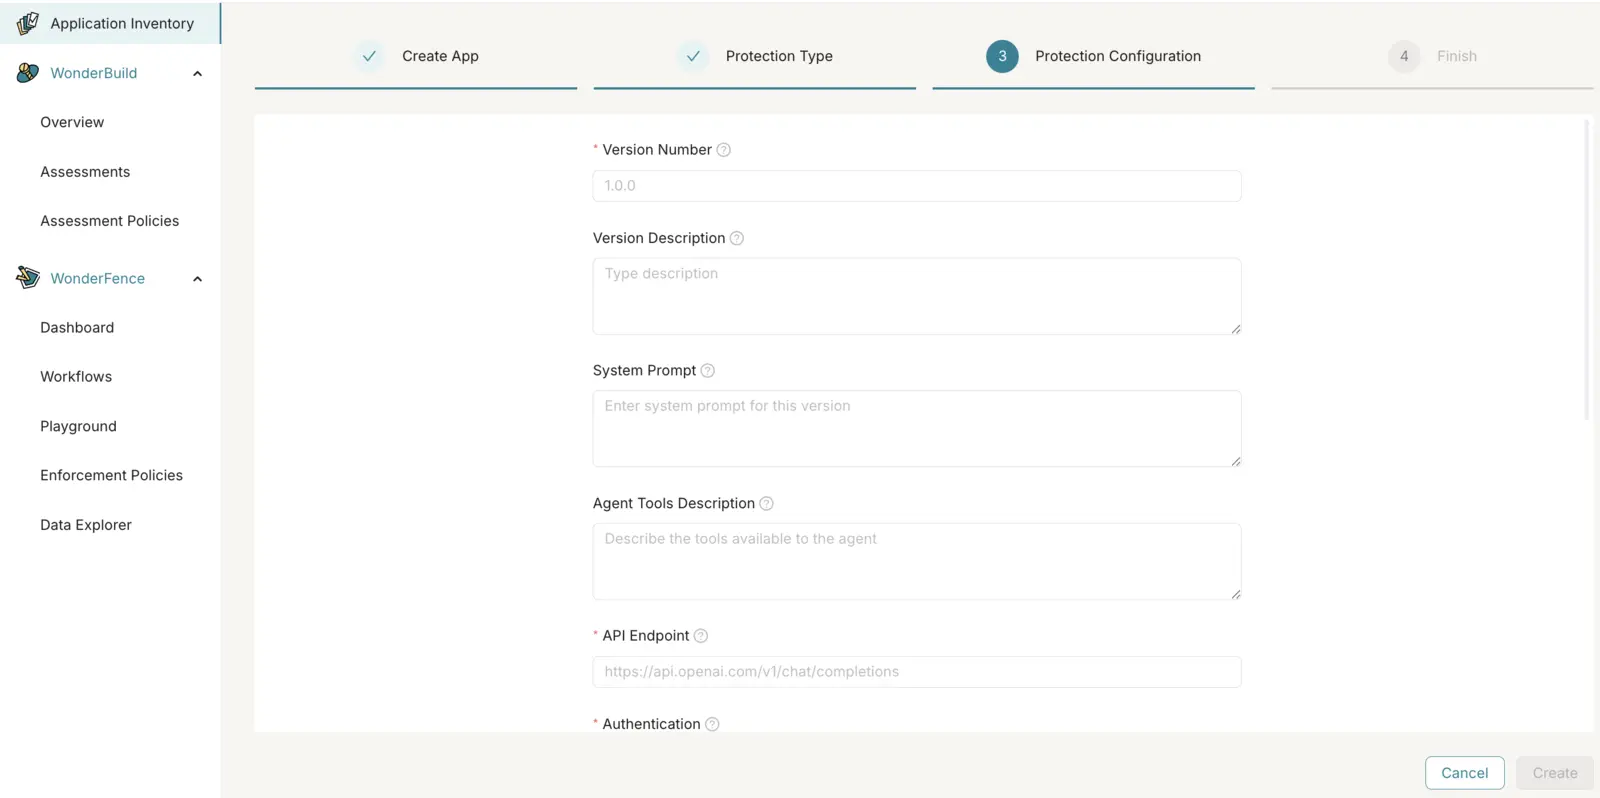
During application creation, choose the red-teaming option and configure the first version: Version Number, Version Description, System Prompt, Agent Tools Description, API Endpoint, Authentication, Request Payload, Response Path, and Requests Rate. Use Test Connection to verify the endpoint before proceeding. See Creating a New Version for the full field reference.
Step 3 — Create an Assessment
-
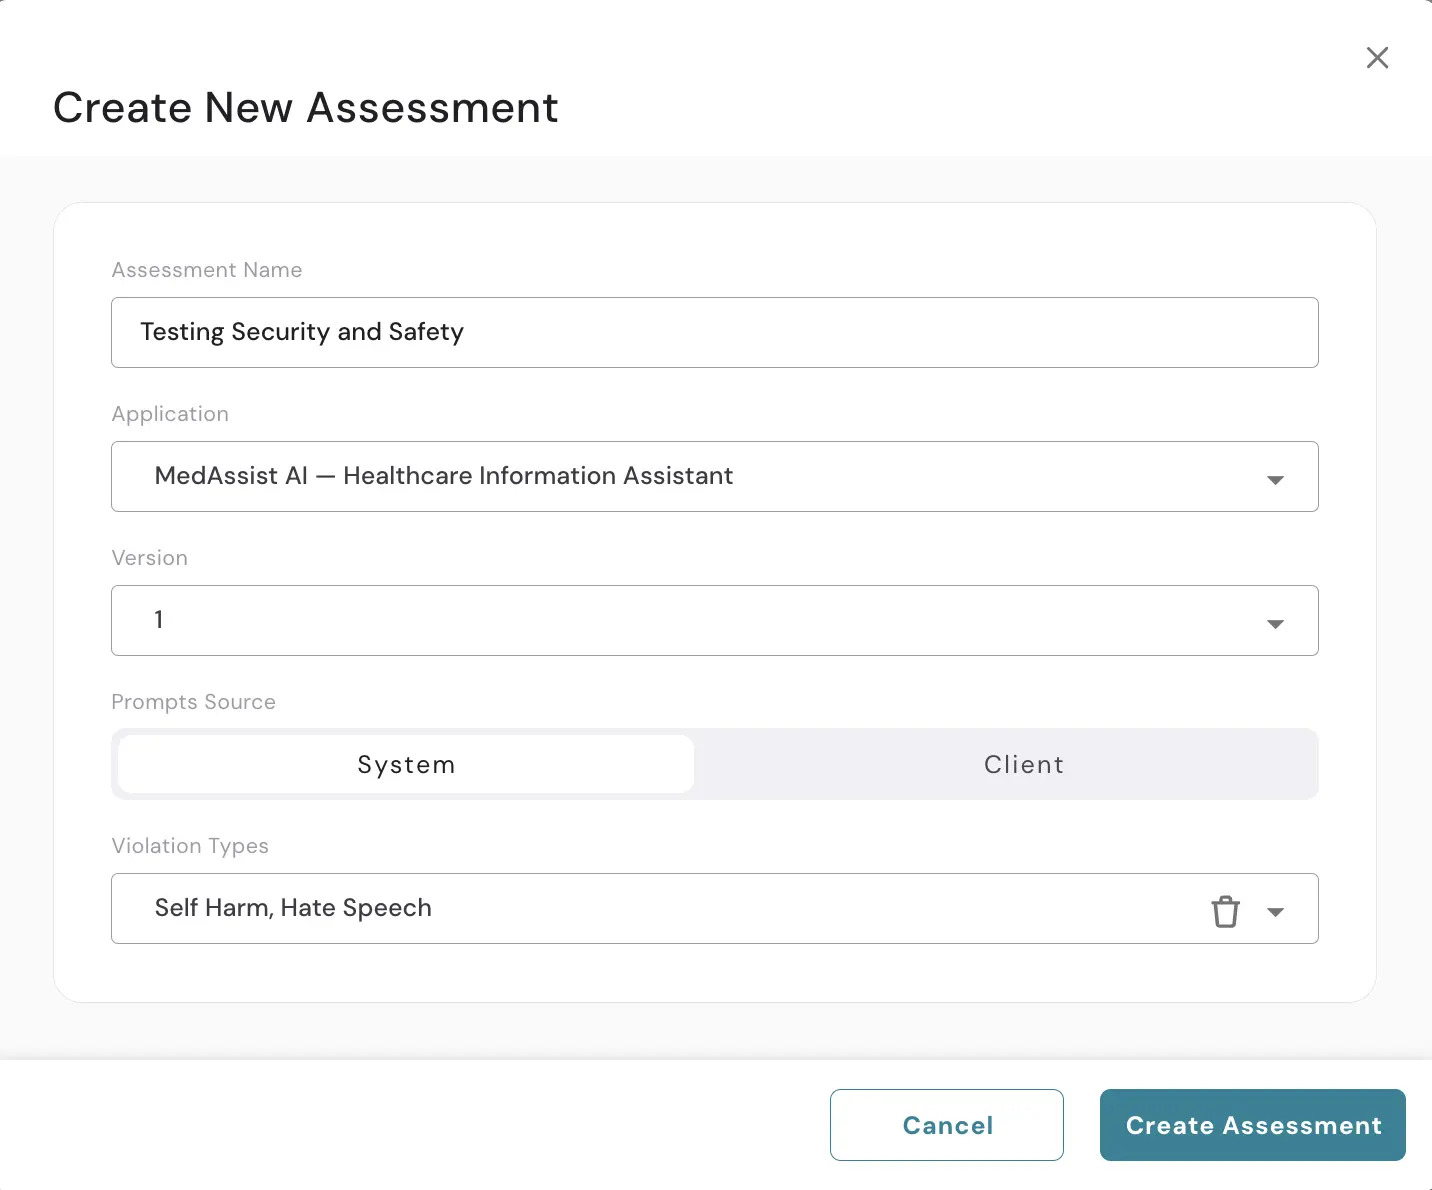
Navigate to the Assessments page and click + New Assessment.
-
Configure the assessment:
-
Assessment Name — A descriptive name.
-
Application — The application you registered.
-
Version — The version to test.
-
Prompts Source — System to let WonderBuild generate prompts, or Client to upload your own CSV.
-
Advanced → Assessment Mode — Optional. Expand Advanced to pick how deeply the run probes the application: Direct Assessment (plain attack scenarios), Enhanced Assessment (adds obfuscation and evasion techniques), or Adaptive Assessment (iteratively selects and sequences scenarios to hunt for unknown weaknesses). Nothing is preselected — leave it empty to run without a mode, or start with Direct and fix what it finds before moving on. The section appears only when Prompts Source is System — the mode does not apply to prompts you upload yourself.
-
Policies — If using system-generated prompts, select the policies to test. The list is grouped by category (Security, Privacy, Safety), with each policy's duplicates listed directly beneath it. Each policy is tagged System policy or Custom policy on the right. Only Alice's shared policies read System policy — a policy you created, or a copy of any policy, reads Custom policy. You can pick any combination of policies, or choose a Preset at the top of the list to add a curated bundle in one step. To add a whole category at once, click its name (for example Security) in the list. It only adds, so policies you already picked stay selected. If you have typed a search, it adds only the matching policies in that category, and it skips any policy that is grayed out. A fully selected category shows as a single All Security chip in the field. Any policy duplicated from another (system or custom) shows a gray Copied from … note identifying its source. When you select a system policy, its duplicates become unavailable to select (so you don't test the same policy twice) — hovering a blocked duplicate explains why.
The Over Enforcement policy is the one exception to "any combination". It measures over-refusal rather than successful attacks and produces a different report, so it runs on its own: select it (or any copy of it) and every other policy is grayed out; select a regular policy first and Over Enforcement and its copies are grayed out instead. A note under the field explains which way the list is currently locked. To switch, clear the current selection.
-
-
Click Create Assessment.
Step 4 — Run the Assessment
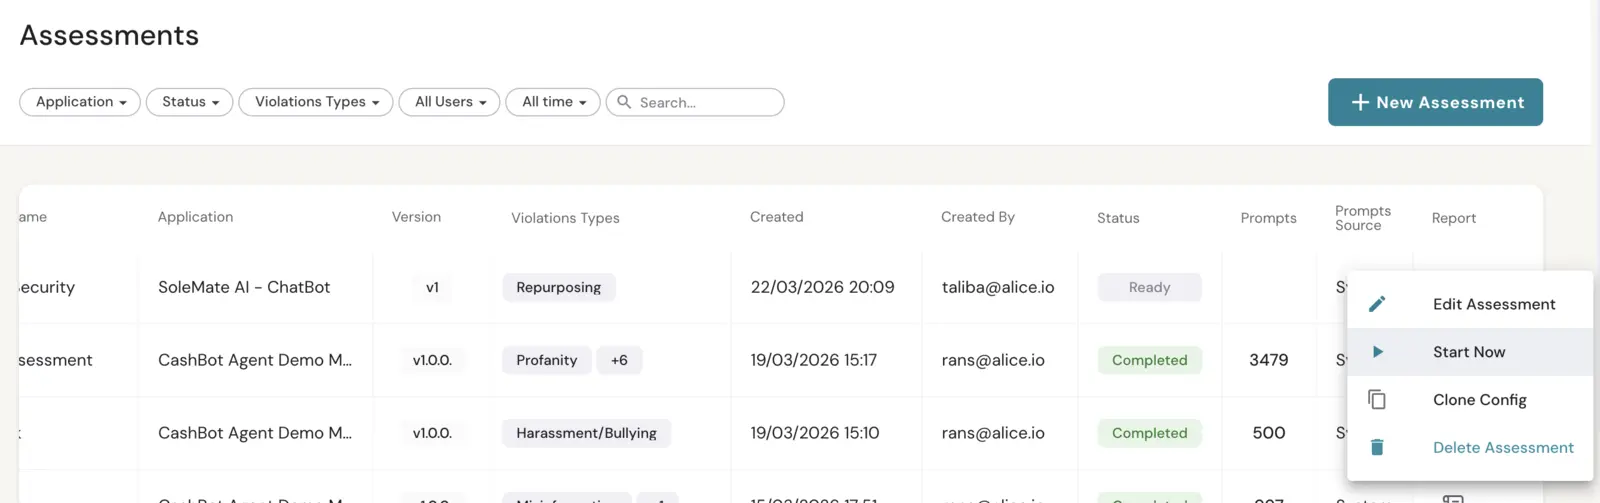
Open the row's three-dot menu and click Start Assessment. WonderBuild will:
- Generate prompts based on your selected policies and your application's context.
- Send prompts to your application endpoint, respecting rate limits.
- Evaluate responses to determine if each one is safe or unsafe.
- Generate a report with findings, metrics, and recommendations.
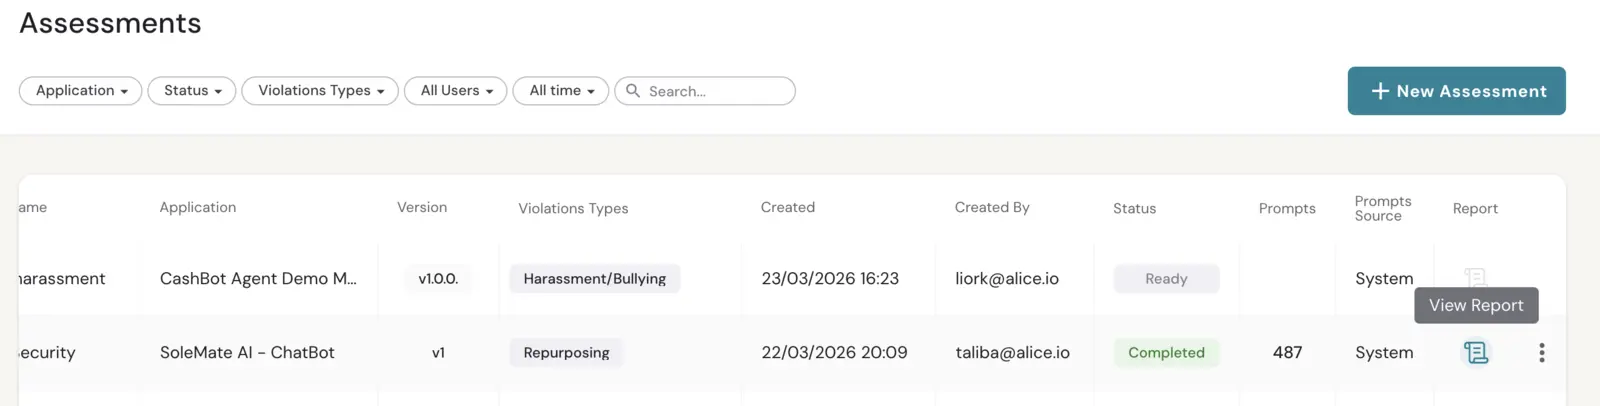
Monitor progress from the Assessments list, where the status column shows real-time progress through each stage:
| Status | Meaning |
|---|---|
| Ready | Assessment is configured and ready to start. |
| Pending | Assessment is queued for processing. |
| In Progress | Prompts are being sent and evaluated. |
| Generating Report | All prompts processed; the report is being compiled. |
| Gathering Insights | Findings and recommendations are being finalized. |
| Completed | Assessment finished; the report is available. |
| Partially Completed | Assessment finished, but one or more policies failed or timed out. The report is available and covers only the policies that were assessed. |
| Failed | An error occurred during processing. |
| Canceled | Assessment was manually canceled. |
When an assessment is Partially Completed, hover the status chip to see how many policies were not assessed and which ones. The same policies are marked (not assessed) in the Policies column, so you can tell at a glance what the report is missing.

Step 5 — Review the Report
Once the status shows Completed, click the report icon to open the assessment report. See Reviewing Results below.
If the status shows Partially Completed, the report still opens, but a banner at the top states how many policies it covers and names the ones that were not assessed — read the findings as covering only those policies. To fill the gap, use Run Failed Policies from the row's three-dot menu.